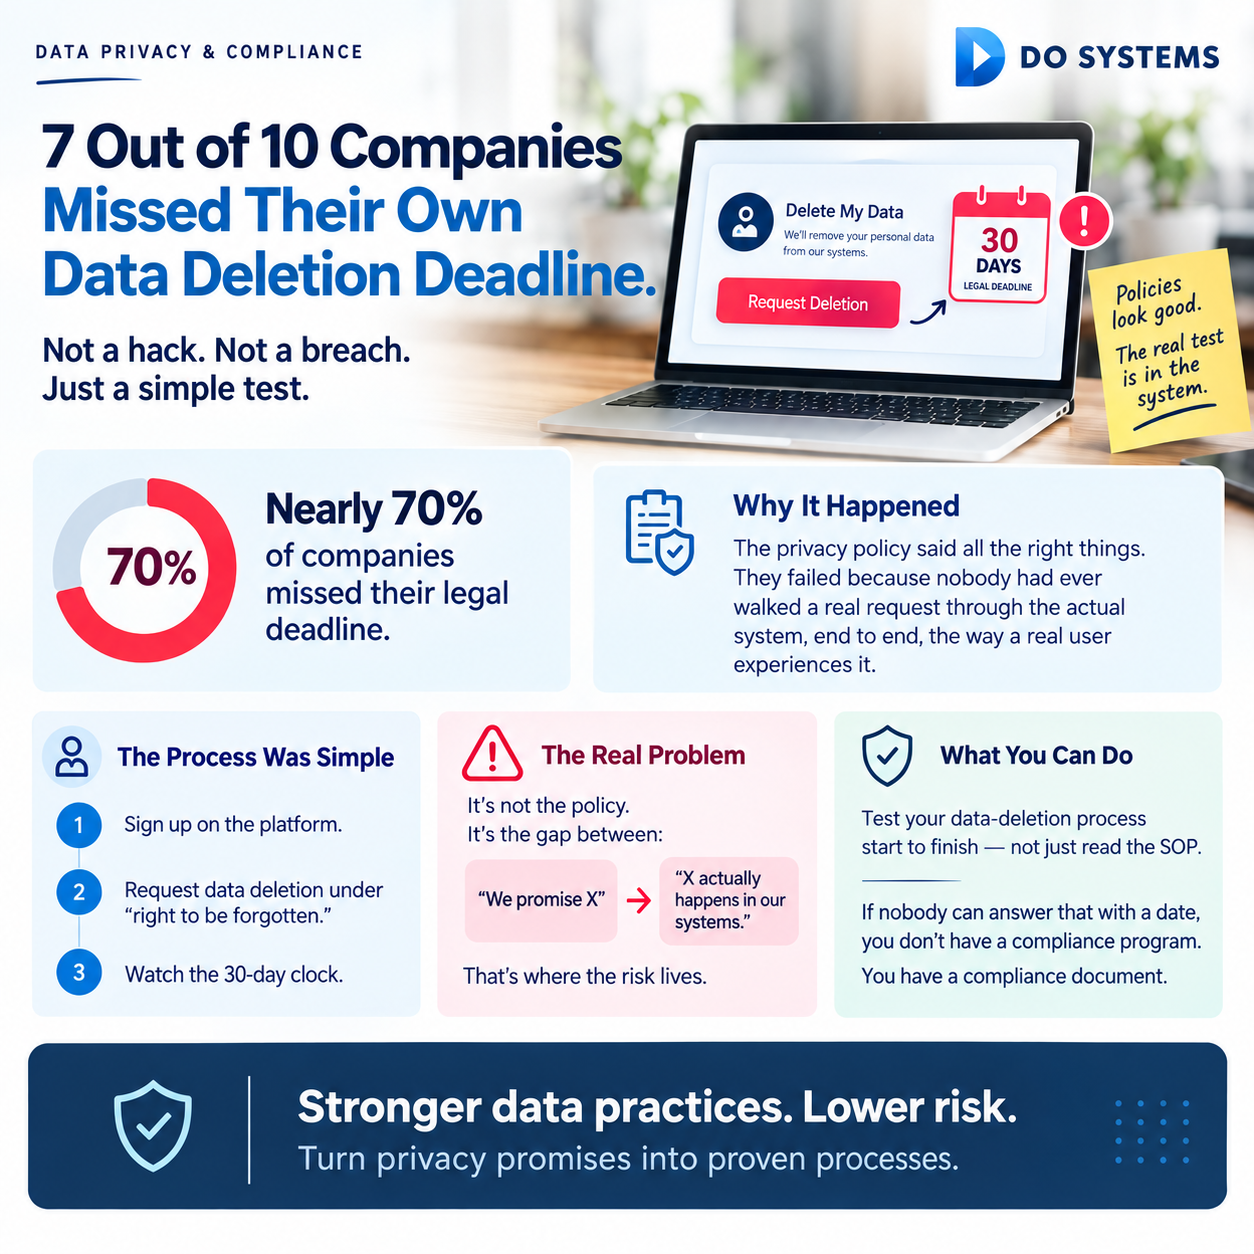
Many companies have privacy policies that promise customers the ability to delete their personal data.
But having a policy is not the same as being able to execute it.
A recent experiment used AI agents to send real data-deletion requests to companies. The results highlighted a familiar problem: companies can have documented privacy processes while the actual request gets lost, delayed, or never completed. The experiment is a useful signal, but its sample and methodology should not be treated as a representative industry statistic.
The Gap Between Policy and Reality
The important question isn’t:
“Do we have a data-deletion policy?”
It’s:
“What actually happens when a real customer requests deletion?”
That process may involve customer support, identity verification, databases, third-party services, backups, internal approvals, and confirmation emails.
If nobody has tested the entire workflow recently, there may be a significant gap between what the company promises and what its systems actually do.
Test Your Compliance Process
A practical approach is to run controlled, end-to-end tests:
- Submit a real test deletion request.
- Track every system and team involved.
- Measure response and completion times.
- Verify that the data was actually removed.
- Check whether third-party systems are handled.
- Record failures and improve the workflow.
Compliance shouldn’t live only in a document. It should work in production.
At DoSystemsInc, we use AI-assisted testing and monitoring to help organizations identify operational gaps in privacy workflows before they become customer or regulatory problems.
The question to ask your team: When was the last time you actually tested your data-deletion process from request to completion?
Comments are closed