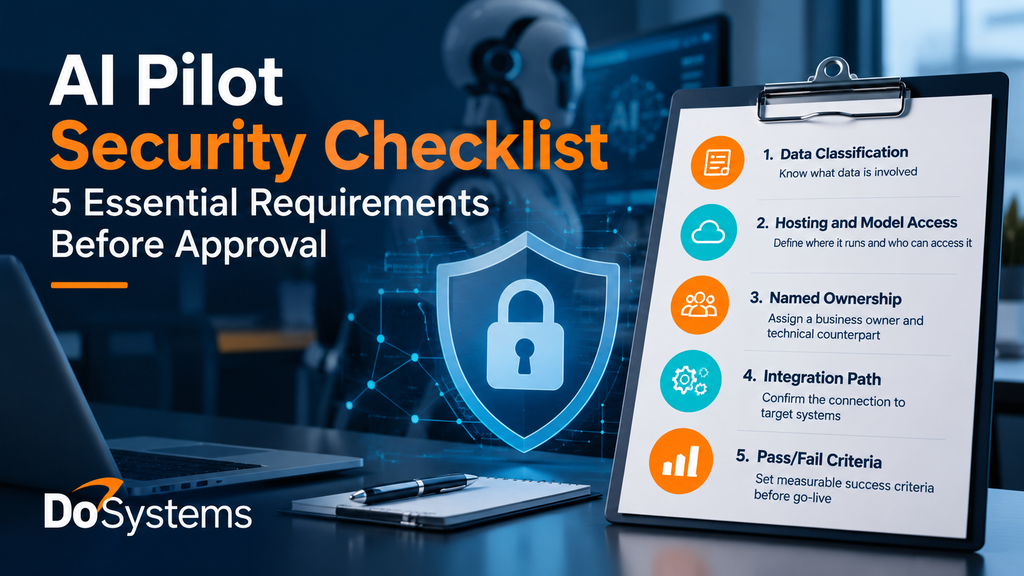
Quick answer: An AI pilot security checklist helps security teams approve AI initiatives by requiring five things upfront: data classification, hosting and model-access rules, accountable ownership, a confirmed integration path, and measurable pass/fail criteria. Without these requirements, pilot reviews can stall for months, or critical security decisions can be overlooked.
Table of Contents
Security Isn’t the Bottleneck. The Request Is.
Security teams often get blamed for slowing down AI pilots. But the real problem frequently begins before a request even reaches the security desk.
When a pilot request arrives without data classification, a named owner, or an integration plan, there is nothing concrete to approve against.
Without a standard AI pilot security checklist, every request can become a separate negotiation, with decisions made case by case.
With a consistent review process, security teams can identify missing requirements earlier and potentially replace lengthy back-and-forth discussions with a focused approval meeting.
The five requirements below are not simply a compliance exercise. They provide the minimum information security leaders need to approve a pilot or return it with specific, actionable feedback.
1. Require Data Classification Before AI Pilot Approval
Every AI pilot security checklist should begin with data classification.
Identify the information the proposed AI system will access and classify it as public, internal, confidential, or regulated.
Document these classifications before approving the pilot.
Skipping this step does not eliminate the decisions that depend on it. It only delays them.
Security teams still need to determine:
Where the data can be stored and processed.
Who can access the information and AI-generated outputs.
Whether sensitive information can be shared with external providers.
Whether legal or compliance approval is required.
If classification takes place after launch, these decisions must be made while the pilot is already operating.
That increases the risk of discovering restrictions only after implementation has begun.
For example, if the workflow involves protected health information subject to HIPAA, the relevant restrictions and safeguards must be identified before data is processed.
An effective AI pilot security checklist makes these requirements explicit rather than leaving them to be discovered during development.
2. Define Hosting and Model Access Requirements
Before approving an AI initiative, security teams must understand where the model operates and how information moves through the system.
The approval request should clearly explain:
Where the AI model is hosted.
Where data is stored and processed.
Whether information leaves the organization’s environment.
Who can access the model and its outputs.
What information is logged.
How prompts and generated responses are retained or deleted.
These decisions should not be postponed until implementation.
Hosting arrangements influence whether a proposed workflow can satisfy the organization’s security, privacy, and regulatory requirements.
For example, a business processing confidential customer records may require specific restrictions on third-party model access.
Model access also needs clear boundaries. Security teams should determine who can submit requests, access outputs, and review activity logs.
A vendor that cannot explain these arrangements should resolve those gaps before the pilot proceeds.
Including these requirements in the AI pilot security checklist helps identify potential security and compliance problems before development begins.
Organizations can also refer to the NIST AI Risk Management Framework for guidance on identifying, evaluating, and managing AI-related risks before
deployment. This provides an additional reference for teams reviewing their AI pilot security checklist.
3. Assign a Business Owner and Technical Counterpart
Every AI initiative needs clear accountability.
An AI pilot security checklist should require two named individuals:
Business owner: Responsible for the operational outcome, business requirements, and success criteria.
Technical counterpart: Responsible for technical implementation, system integration, and security coordination.
Listing a department instead of an individual is not sufficient.
Without clear ownership, issues can remain unresolved while teams determine who should make a decision.
For example, if an AI assistant begins producing unreliable recommendations, someone must have the authority to pause the workflow, investigate the problem, and approve corrective action.
When accountability is distributed across multiple departments without a defined owner, those decisions can be delayed.
A successful AI pilot requires people who can respond to operational and technical issues without waiting for another committee meeting.
Documenting both owners in the AI pilot security checklist ensures that responsibility is established before the project begins.
4. Confirm the Integration Path Before Sign-Off
An AI pilot should not receive approval based solely on an impressive demonstration.
Security teams also need to know how the proposed solution will interact with existing enterprise systems.
Identify the system where AI-generated information must be delivered or recorded.
Depending on the workflow, this might include:
Electronic Health Record (EHR) systems.
Enterprise Resource Planning (ERP) platforms.
Customer Relationship Management (CRM) systems.
IT service management and ticketing platforms.
Internal document management systems.
Next, confirm whether the target system provides an approved API or another supported integration method.
This is a critical requirement in the AI pilot security checklist because a solution that works only in a standalone chat interface may not be suitable for production.
Consider an AI assistant that summarizes customer support requests.
If employees must manually copy customer information into a separate AI tool and paste responses back into the company’s support platform, the process can introduce security and operational risks.
The demonstration may look successful, but the workflow remains disconnected from the systems employees actually use.
Confirming the integration path early helps determine whether the proposed pilot has a realistic route to production.
It also allows security teams to assess access permissions, authentication, data movement, and monitoring requirements before deployment.
5. Establish Pass/Fail Criteria Before Go-Live
The final requirement in an AI pilot security checklist is a documented definition of success.
Before the pilot begins, agree on:
The business outcome being measured.
The target performance metric.
The minimum acceptable threshold.
The date when results will be reviewed.
The conditions for continuing, improving, or stopping the pilot.
Without these criteria, success can become subjective.
A pilot might produce an impressive demonstration without delivering measurable operational improvements.
For example, an AI-powered support assistant could be evaluated on response accuracy, average handling time, escalation frequency, and compliance with approved information sources.
The organization should establish acceptable thresholds for the relevant metrics before testing begins.
Security and operational requirements should also be included in the evaluation.
A solution that improves productivity but violates approved access controls should not be considered successful simply because its business metrics look promising.
A documented evaluation process allows teams to make decisions based on agreed evidence rather than presentation quality.
A Missing Answer Is a Gap, Not a Rejection
An incomplete AI pilot request does not automatically mean the initiative should be abandoned.
It means a specific requirement needs attention.
An AI pilot security checklist helps reviewers identify exactly what is missing.
For example:
Data classification incomplete: Identify the data categories and required safeguards.
Hosting rules undefined: Confirm the hosting environment and model-access restrictions.
No technical owner: Assign an accountable individual responsible for implementation and security coordination.
Integration path unconfirmed: Verify the approved connection to the target system.
Success criteria missing: Define measurable outcomes and minimum acceptance thresholds.
This approach makes security reviews more transparent.
Instead of receiving a vague response such as “not ready,” business teams receive a clear explanation of what must be completed before approval.
That clarity can reduce unnecessary delays and discourage teams from bypassing security processes.
The goal is not to reject more AI initiatives. It is to help organizations move forward with well-defined requirements and appropriate safeguards.
What a Pre-Cleared AI Pilot Looks Like
A well-prepared AI pilot request answers all five questions before reaching the final approval stage.
The data has been classified.
Hosting and model-access requirements are documented.
A business owner and technical counterpart are accountable.
The integration path has been reviewed.
Measurable pass/fail criteria have been agreed upon.
With these requirements established, the organization has a clearer foundation for scoping the implementation.
The remaining work involves estimating the technical effort, evaluating data readiness, and identifying operational dependencies.
These details cannot be reliably estimated without examining the specific business process and systems involved.
Using an AI pilot security checklist helps teams prepare that information before investing significant time and resources in development.
The result is a more structured approval process and a clearer understanding of what is required to move from pilot to production.
Turn Your AI Pilot Security Checklist Into an Actionable Plan
Security approval should not require months of uncertainty.
The right process begins with clear requirements, documented responsibilities, and measurable outcomes.
If your organization is evaluating AI initiatives, an AI pilot security checklist can help identify missing information before implementation begins.
At Do Systems, our free 45-minute AI strategy session is designed to help organizations evaluate a specific business process, discuss readiness requirements, and outline a practical implementation approach.
The session can help identify the information needed to scope a potential 6–8 week AI pilot plan, with the actual implementation timeline depending on project requirements, integration complexity, and data readiness.
Ready to move your AI initiative forward with greater clarity?
Free 45-minute AI strategy session
Frequently Asked Questions
What should a security team require before approving an AI pilot?
A security team should use an AI pilot security checklist covering five essential requirements: documented data classification, approved hosting and model-access rules, named business and technical owners, a confirmed integration path, and measurable pass/fail criteria.
These requirements help reviewers understand the proposed workflow and identify unresolved risks before approval.
Why do AI pilot reviews stall or get skipped?
AI pilot reviews can stall when requests arrive without sufficient information about data security, ownership, integration, or expected outcomes.
Without standardized requirements, security teams may need repeated discussions to identify missing details.
A documented checklist helps businesses understand what information is required and allows reviewers to provide specific feedback.
How long does a scoped AI pilot take once security approves it?
An AI pilot’s timeline depends on the complexity of the proposed workflow, integration requirements, data readiness, and security approvals.
A 6–8 week pilot may be suitable for certain well-defined initiatives, but this is not a universal implementation timeline.
The actual duration should be determined during project scoping.
Comments are closed